Skip to content
Close Menu
CryptoAINews
  • Cryptocurrency
  • Blockchain
  • Bitcoin News
  • Altcoins
  • Crypto Market Trends
  • Crypto Mining
  • Ethereum
  • AI News
  • Sponsored
  • Advertise
Trending
  • Ethereum client security fixes leave binary users with a separate Java check
  • Data centers are now a midterm issue, even in Brooklyn
  • Immersive explorations in Gemini app for students and learners
  • Apple CEO says the company doesn’t ‘want to ship AI for AI’s sake’
  • Centrifuge USDS Rate Increase Verification: 3.76% Jump
  • Tether-Backed FASE Foundation Targets Scams and Stablecoin Aid
  • Ads in AI Mode expand to 10 new countries
  • OpenAI reportedly lowers funding target for new round
  • AI News
  • Cryptocurrency
  • Blockchain
  • Bitcoin News
  • Altcoins
  • Crypto Market Trends
  • Crypto Mining
  • Ethereum
  • Sponsored
  • Advertise
CryptoAINews
  • Cryptocurrency
  • Blockchain
  • Bitcoin News
  • Altcoins
  • Crypto Market Trends
  • Crypto Mining
  • Ethereum
  • AI News
  • Sponsored
  • Advertise
CryptoAINews
Home » Ethereum » Ethereum client security fixes leave binary users with a separate Java check
ethereum certificate trust risk
Ethereum

Ethereum client security fixes leave binary users with a separate Java check

CryptoAINewsBy CryptoAINewsNovember 1, 2026No Comments3 Mins Read
Share
Facebook Twitter LinkedIn Pinterest Email


Teku and Besu, software program used to run Ethereum nodes, have shipped Docker safety fixes after a certificate-authority compromise at eMudhra. Operators utilizing affected photos can replace these containers. Binary installations want a separate examine of their Java runtime.

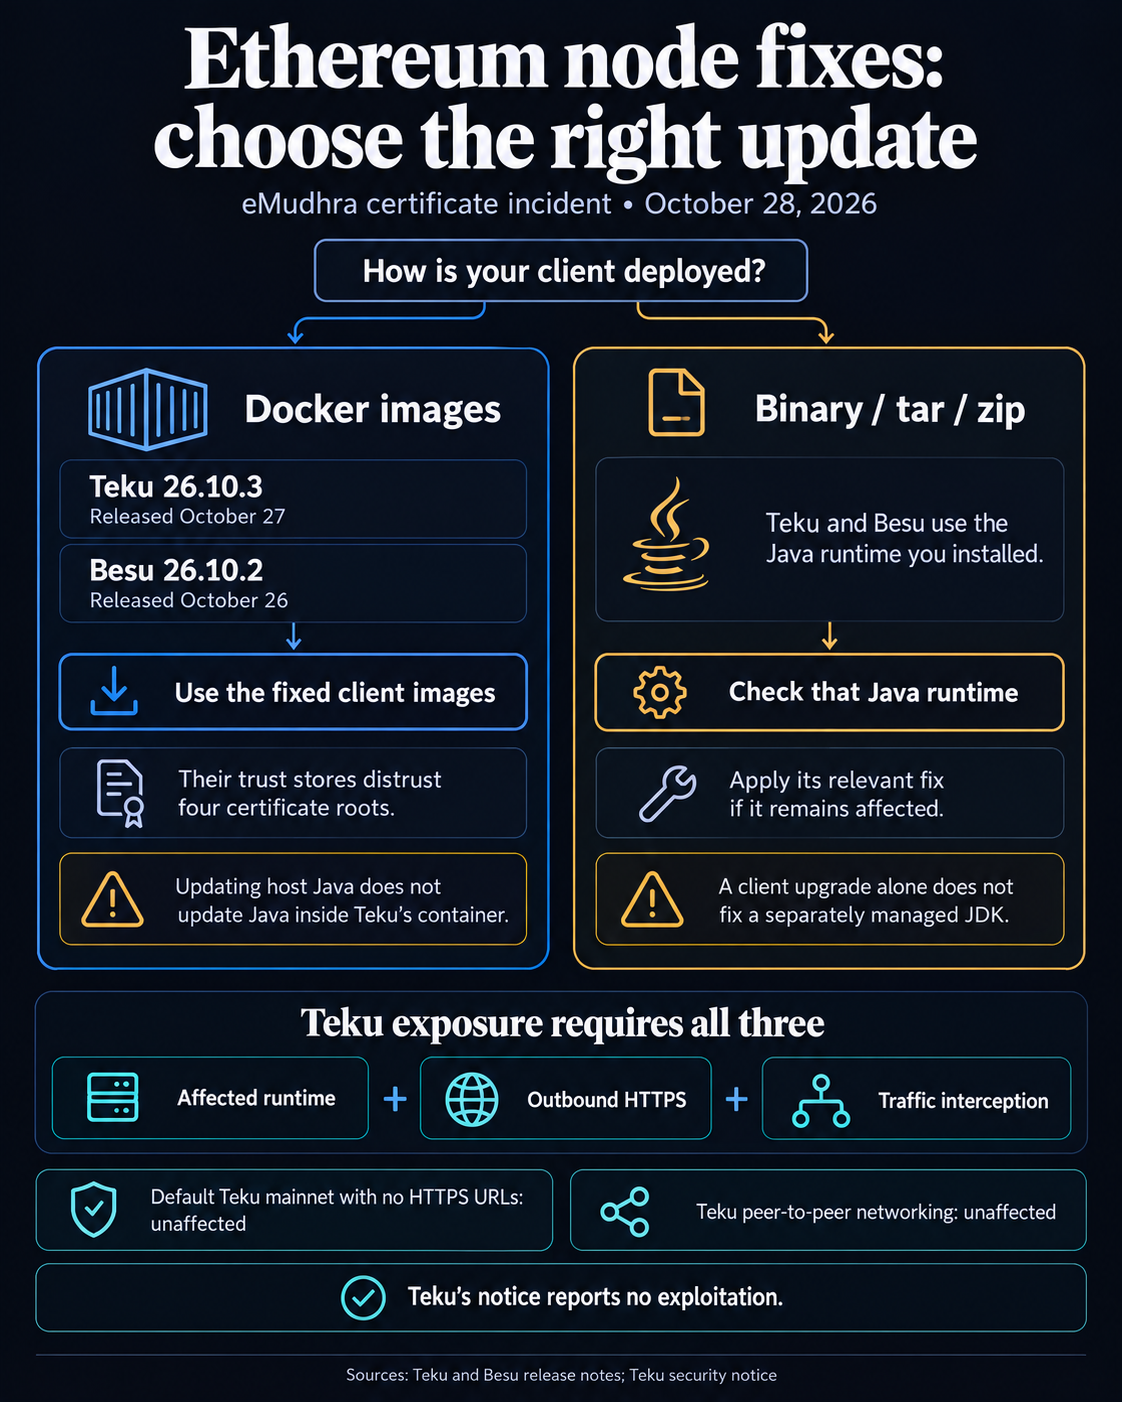
Teku 26.10.3, launched Oct. 27, and Besu 26.10.2, launched Oct. 26, cease their Docker photos trusting 4 certificates roots: emSign ECC Root CA – G3, emSign Root CA – G1, emSign Root CA – G2 and AAA Certificates Providers.

For Teku, publicity is dependent upon configuration. The staff’s security notice says default mainnet nodes with out HTTPS URLs are unaffected. On an unremediated runtime, an attacker would want to intercept an affected HTTPS connection to impersonate its endpoint. The discover studies no exploitation.

The underlying incident concerned recoverable non-public keys for eight emSign G3 intermediate certificates authorities. eMudhra acknowledged a script error that produced weak keys and mentioned the intermediates have been revoked after the Oct. 17 report. Teku’s advisory says Java doesn’t examine revocation by default, so affected runtimes nonetheless want their very own remediation.

Related Reading

Crypto security chiefs sound alarm as PHP emergency patch scrambles devs worldwide

What operators have to examine

The brand new shopper photos tackle their bundled belief shops, the lists of certificates authorities Java accepts. Teku’s discover identifies all its Docker photos via 26.10.2, together with the -jdk25 and -jdk26 variants, as retaining the implicated emSign ECC root. Updating Java on the host doesn’t change the runtime inside these containers.

Besu explicitly limits its root-removal change to Docker photos: its tar/zip customers should have a JDK that trusts the roots. Teku’s binary distribution likewise makes use of the Java runtime put in by its operator. These installations want that runtime checked and, if it stays affected, mounted individually from the shopper software program.
The Catalyst

Every day E-newsletter

Know what’s shifting crypto.

Begin with the tales that matter. Get the context behind the headlines and a transparent view of what to look at subsequent.

catalyst newsletter scrapbook v3

Deployment decision for Ethereum node operators: use fixed Teku 26.10.3 or Besu 26.10.2 Docker images; separately installed Java needs checking and remediation if affected. Teku exposure requires an affected runtime, outbound HTTPS and traffic interception.Deployment decision for Ethereum node operators: use fixed Teku 26.10.3 or Besu 26.10.2 Docker images; separately installed Java needs checking and remediation if affected. Teku exposure requires an affected runtime, outbound HTTPS and traffic interception.

Teku’s HTTPS dependencies can embrace distant signers, beacon nodes, execution purchasers and builders or relays, in addition to proposer configuration, startup knowledge and metrics providers. The discover additionally flags Sepolia, Hoodi and Ephemery, which obtain beginning state over HTTPS when launched with an empty database.

Related Reading

Ethereum’s long-awaited Glamsterdam upgrade hits another roadblock as 13 security risks emerge

On an unremediated runtime, an attacker who intercepts the connection might impersonate a distant beacon node. That would redirect proposal charges or trigger missed validator duties. An attacker impersonating an uncovered exterior signer might get hold of signatures for validator exits. The discover says mutual TLS shopper authentication on the signer limits its affect to denial of service.

Teku’s peer-to-peer networking, together with libp2p and discv5, doesn’t use certificates authorities and is outdoors this situation.

Related Reading

Lightning tightens invoice rules after reported attack made Bitcoin withdrawals look unpaid


Source link

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
CryptoAINews
  • Website

Related Posts

North Korea secretly turned crypto firms into a funding source

October 30, 2026

Bitcoin and Ether options reach eligible Kraken EEA traders

October 28, 2026

Lido’s 32 ETH operator bond

October 26, 2026

Ethereum’s long-awaited Glamsterdam upgrade hits another roadblock as 13 security risks emerge

October 24, 2026
Add A Comment

Comments are closed.

About us

CryptoAINews is an independent digital publication focused on cryptocurrency, blockchain, and artificial intelligence news.

The platform is owned and operated by Robert Grabarevic, providing timely news coverage, market updates, and educational content for a global audience interested in emerging technologies and digital finance.

CryptoAINews is committed to transparent reporting, responsible publishing, and delivering informative content based on publicly available data, verified sources, and industry developments.

All content published on this website is for informational purposes only and does not constitute financial or investment advice.

Top Insights

Ethereum client security fixes leave binary users with a separate Java check

November 1, 2026

Data centers are now a midterm issue, even in Brooklyn

November 1, 2026

Immersive explorations in Gemini app for students and learners

November 1, 2026
Categories
  • ! Без рубрики
  • Advertise
  • AI News
  • Altcoins
  • Betano España
  • Bitcoin News
  • Blockchain
  • Crypto Market Trends
  • Crypto Mining
  • Cryptocurrency
  • Ethereum
  • Game
  • Games
  • God of Casino Ελλάδα
  • Pin Up
  • public
  • Spinlander Danmark
  • Sponsored
  • Superbet Ελλάδα
  • Imprint-Legal-Notice
  • Author / Publisher Bio
  • Privacy Policy
© 2025 CryptoAINews – Owned & Operated by Robert Grabarevic

Type above and press Enter to search. Press Esc to cancel.